de.yaacc.share.StreamIntake Class Reference
The checks a browser activity repeats on a shared file it receives. More...
Collaboration diagram for de.yaacc.share.StreamIntake:
Static Public Member Functions | |
| static String | validate (String action, int clipItemCount, String clipItemZeroUri, boolean hasData, int intentFlags, String ownAuthority, Predicate< String > isOwnProviderAuthority) |
Static Public Attributes | |
| static final int | READ_FLAG = 0x1 |
Intent.FLAG_GRANT_READ_URI_PERMISSION, as a number so this class stays free of android.*. | |
Detailed Description
The checks a browser activity repeats on a shared file it receives.
The launcher forwards a file only after its own checks, but TabBrowserActivity is exported, so any app can start a browser directly with any intent: nothing is trusted because "it came from the
launcher". Plain Java, no android.*; the glue reads the fields from the Intent.
A share is accepted only if ALL hold:
-
the action is exactly
android.intent.action.SEND; -
the ClipData has exactly ONE item (the system checks the grant for every ClipData item, never for
EXTRA_STREAM, so the one URI is read from item 0 only); -
the intent has no
data; -
the intent's own flags carry
READ_FLAG(a read grant that really arrived with this intent; without it the system did not check that the sender holds access); -
SharedContentPolicy#isAcceptableUriaccepts the text (acontent:URI of another app); -
the authority is not a provider of this app (any of our providers, not only the file provider), judged by
isOwnProviderAuthority; if that check throws, the share is refused.
Member Function Documentation
◆ validate()
|
static |
- Parameters
-
action the intent's action, may be null clipItemCount the number of ClipData items, 0 for no ClipData clipItemZeroUri the URI of ClipData item 0 as text, may be null hasData true if the intent has a dataURIintentFlags the intent's own flags ownAuthority the authority of yaacc's file provider isOwnProviderAuthority true if an authority belongs to a provider of this app
- Returns
- the URI text to keep as the pending share, or null to ignore the intent
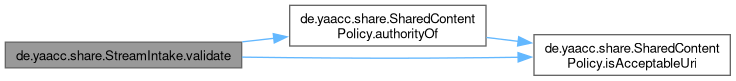
Here is the call graph for this function:
The documentation for this class was generated from the following file:
- /github/workspace/yaacc/src/main/java/de/yaacc/share/StreamIntake.java
Generated by
 1.12.0